Unauthenticated Admin API Access via HTTP Verb Tampering
Wayback Machine recon led to hidden admin endpoints. A simple switch from GET to POST bypassed all access controls, leaking thousands of customer records from a REACTED promotion campaign.
AI Engineering • Generative AI • AI Security
I'm Mohamed Zahir, a Master's student in Artificial Intelligence and Emerging Technologies focused on AI Engineering, Generative AI, and secure AI systems. I build practical AI and machine-learning projects while exploring how AI-powered applications can be tested and secured. I document my projects, experiments, research, and technical learning here.
Wayback Machine recon led to hidden admin endpoints. A simple switch from GET to POST bypassed all access controls, leaking thousands of customer records from a REACTED promotion campaign.

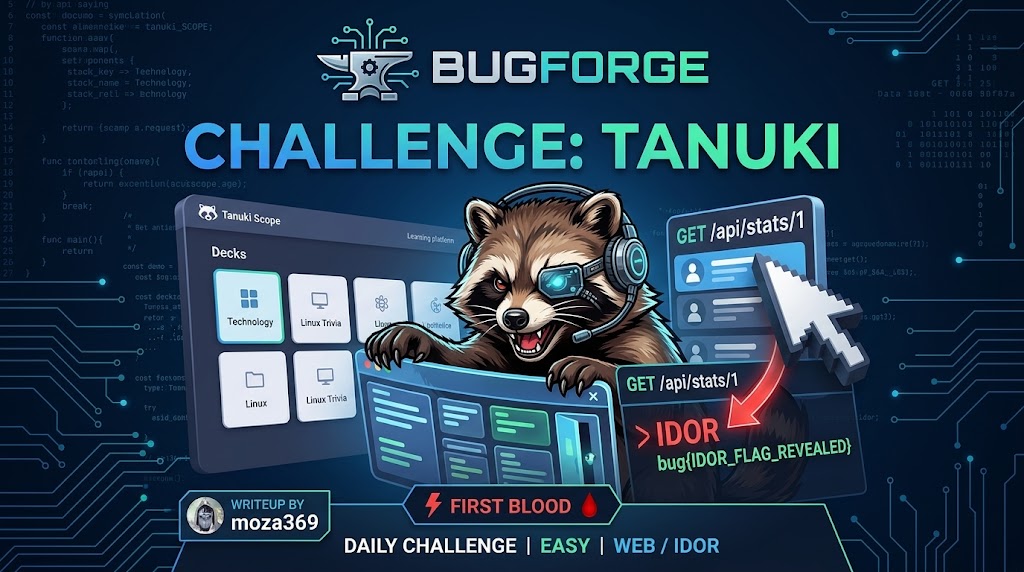
A web application challenge highlighting an Insecure Direct Object Reference (IDOR) flaw. It demonstrates how manipulating a numeric identifier in an API endpoint (/api/stats/:id) bypasses missing backend authorization checks to leak other users' sensitive study statistics and capture the flag..
A previously reported AWS credentials leak was marked as resolved, but the credentials were never rotated. I verified they still worked and could inject data into the production logging stream.

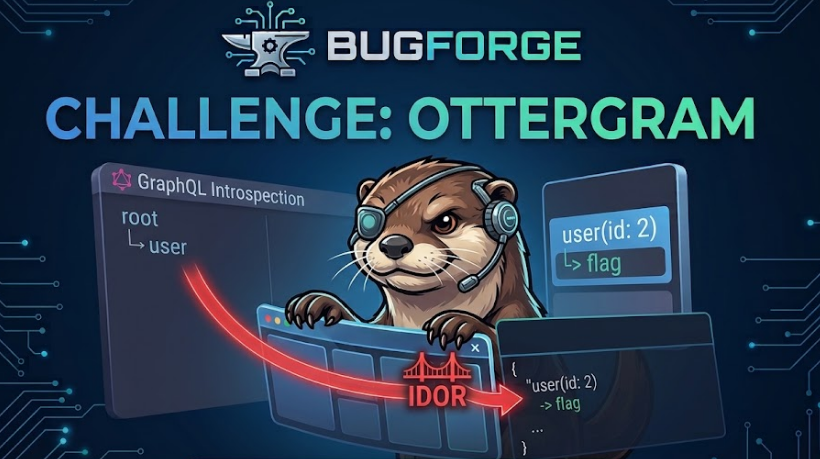
The Ottergram challenge on BugForge is an easy-level web vulnerability lab centered on exploiting a misconfigured GraphQL endpoint. Players must leverage enabled introspection to map the database schema, identify poor object-level access controls, and perform an IDOR attack by manipulating user identifiers to access administrative accounts and recover a hidden flag.

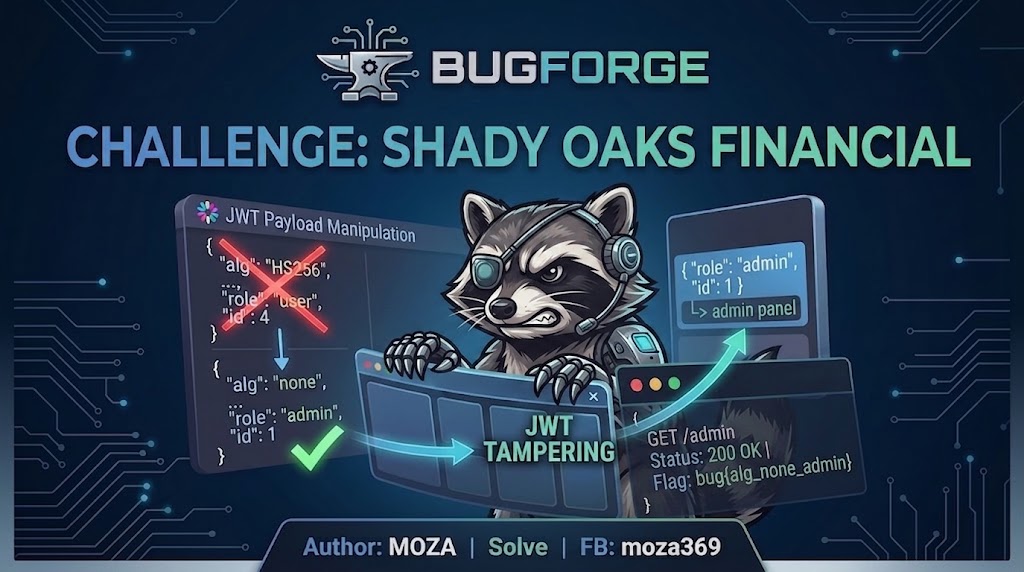
An easy-level web vulnerability challenge focused on JWT privilege escalation. It demonstrates how improper signature validation and insecure client-side token management allow users to manipulate roles and IDs to bypass access controls, reach the admin panel, and retrieve the flag.
A car marketplace contact form rendered HTML in email notifications — I hesitated to report it, but it turned out to be a valid finding.
Capture The Flag writeups from Root-Me, BugForge, NahamCon, and more.
→Security research, AI experiments, and technical investigations.
→AI Engineering, Generative AI, AI Security, and selected technical projects.
→Technical write-ups from security research, CTFs, and personal labs.
→I'm currently pursuing a Master's degree in Artificial Intelligence and Emerging Technologies, focused on AI Engineering, Generative AI, and secure AI systems. My cybersecurity background gives me a strong foundation for exploring how AI-powered applications can be built, tested, and secured.
Learn more about me →